Ransom X Ransomeware attacks Texas Department of Transportation TxDOT

Ransomware | What Is and Different Types of Ransomware

Ransom X Ransomeware attacks Texas Department of Transportation TxDOT

RansomX is a new ransomware used actively in human-operated and targeted attacks against government agencies and enterprises.

In May 2020 two Texas state agencies were attacked, the Texas Court and the Texas Department of Transport(TxDOT) were hit by a ransomware attack.
At the time of the attacks , it was not known what ransomware targeted the agencies

RANSOM X

This is a human-operated ransomeware, rather than one distributed via phishing or malware, when executed the ransomware will open a console that displays information to the attacker while it is running.
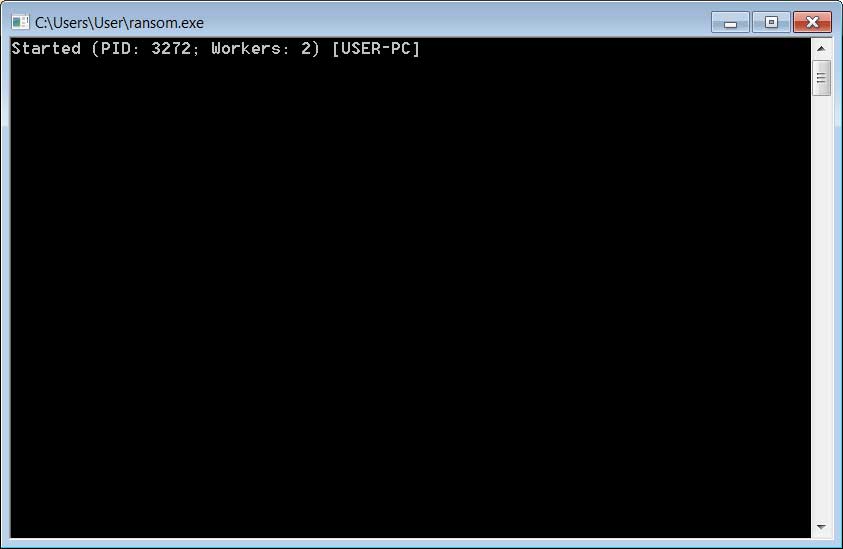
Ransom Exx console

This ransware bypass various windows system folders and any files that match the follow extensions:


.ani, .cab, .cpl, .cur, .diagcab, .diagpkg, .dll, .drv, .hlp, .icl, .icns, .ico, .iso, .ics, .lnk, .idx, .mod, .mpa, .msc, .msp, .msstyles, .msu, .nomedia, .ocx, .prf, .rtp, .scr, .shs, .spl, .sys, .theme, .themepack, .exe, .bat, .cmd, .url, .mui
By bypassing these folders, it gives room for attackers to encrypt a computer while also attacking
other computers on the network without fear their tools will become encrypt.

Ransom X also perform a series of commands throughout the encryption process that:

  • Delete NTFS journals
  • Disable Windows Recovery environment
  • Delete Windows backup catalogs
  • Deletes Windows backup catalogs
  • Clears Windows event logs
  • Wipe free space from the Local drives.
Below is an example of the Texas Department of Transport attack was .txdot.
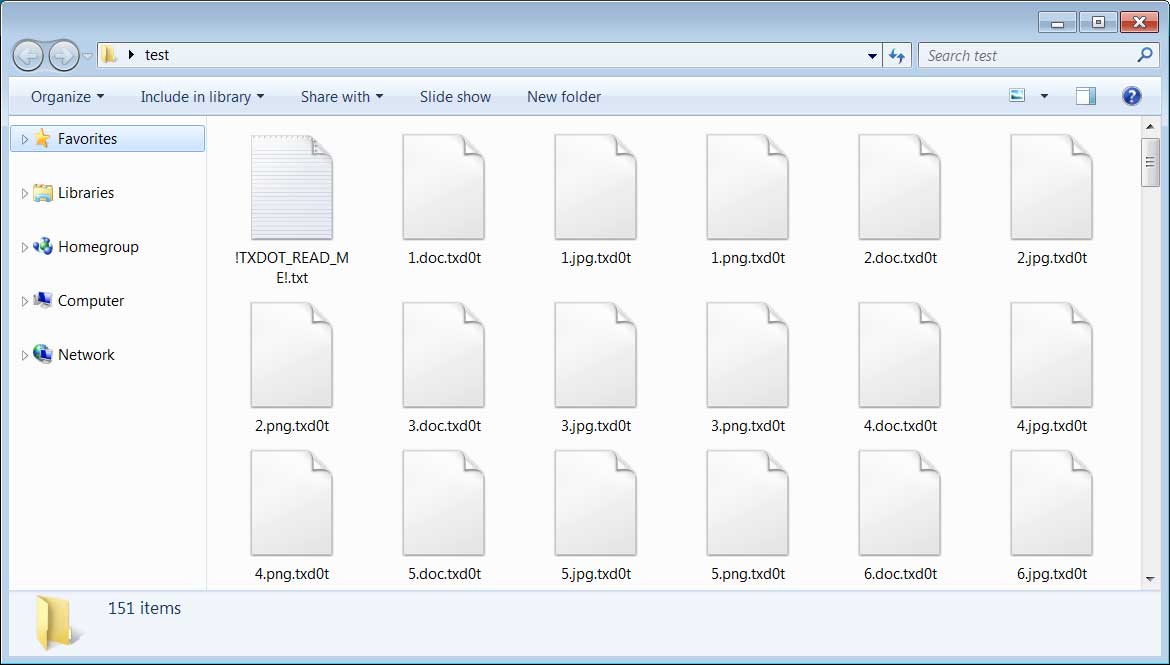
Ransom Exx encrypted files


Comments

Popular posts from this blog

MY PEOPLE PLEASE I NEED YOUR ADVICE   Robbers enter a house, asks for all the money and valuables. After they collect what they can, they give the man of the house a gun with instructions to shoot his wife or else he be shot himself. The man gets the gun, points it at his wife and hesitates. He is thinking of what he has gone through in life with his wife and how she has suffered and sacrificed for him. He hands back the gun and says, “I am sorry I can’t do this… “The boss of the robbers silently grabs the gun from him and passes it on to the wife with the same instruction. The wife gets the gun and without any single hesitation points to her husband’s head and pulls the trigger. But alas, the gun had no bullets in it. The robbers get their gun and walk out of the house laughing. QUESTIONS FOR DISCUSSION 1. If you were the man in that house how would you react towards your wife? 2. If you were the wife, what explanation can you...
 Who Are You Trying to Impress? Can you imagine viewing criticism as ‘a very small thing’? Or being liberated from the need to impress people; your self-esteem no longer dependent on someone noticing how successful, smart, or attractive you are?  Think what it would be like to feel genuine love for someone who expresses their disapproval of you.  Is such a life even possible? With God’s help, yes!  One pastor says: ‘Years ago I wanted to lead a certain ministry. When I wasn’t chosen I became angry. Of course I didn’t show it. That’s not to say I didn’t love God. I just wanted to serve me more than Him! By saying no, God was correcting an attitude that would destroy any real ministry I might have later. When you represent God so visibly it’s nearly impossible for anyone to detect that you’re a fake…except God.’ Ever hear of ‘approval addiction’? Its symptoms include living in fear of what others think of you; being easily hurt by what they...
Top 20 Most Asked Third Party Risk Questions for Vendors  These questions help organizations assess the overall risk posed by third-party vendors, covering critical areas like data protection, regulatory compliance, and incident response. Here’s a list of the Top 20 Most Asked Third-Party Risk Management (TPRM) Questions for Vendors in TPRM questionnaires: 1. What types of sensitive data do you handle for our organization? Vendors should clarify the types of data they collect, process, or store, such as personal information, financial data, or intellectual property. 2. How do you protect data at rest and in transit? This question probes into the encryption methods, protocols, and security controls in place for safeguarding data during storage and transmission. 3. Do you have a formal Information Security Program in place? Vendors should describe their overall cybersecurity framework, including policies, procedures, and governance. 4. How do you manage user access to our data and s...